
Verifying Whether an Email Address Is Real Before You Respond
Not every email address in your inbox belongs to who it claims. Here's a structured way to assess authenticity before engaging with unknown senders.
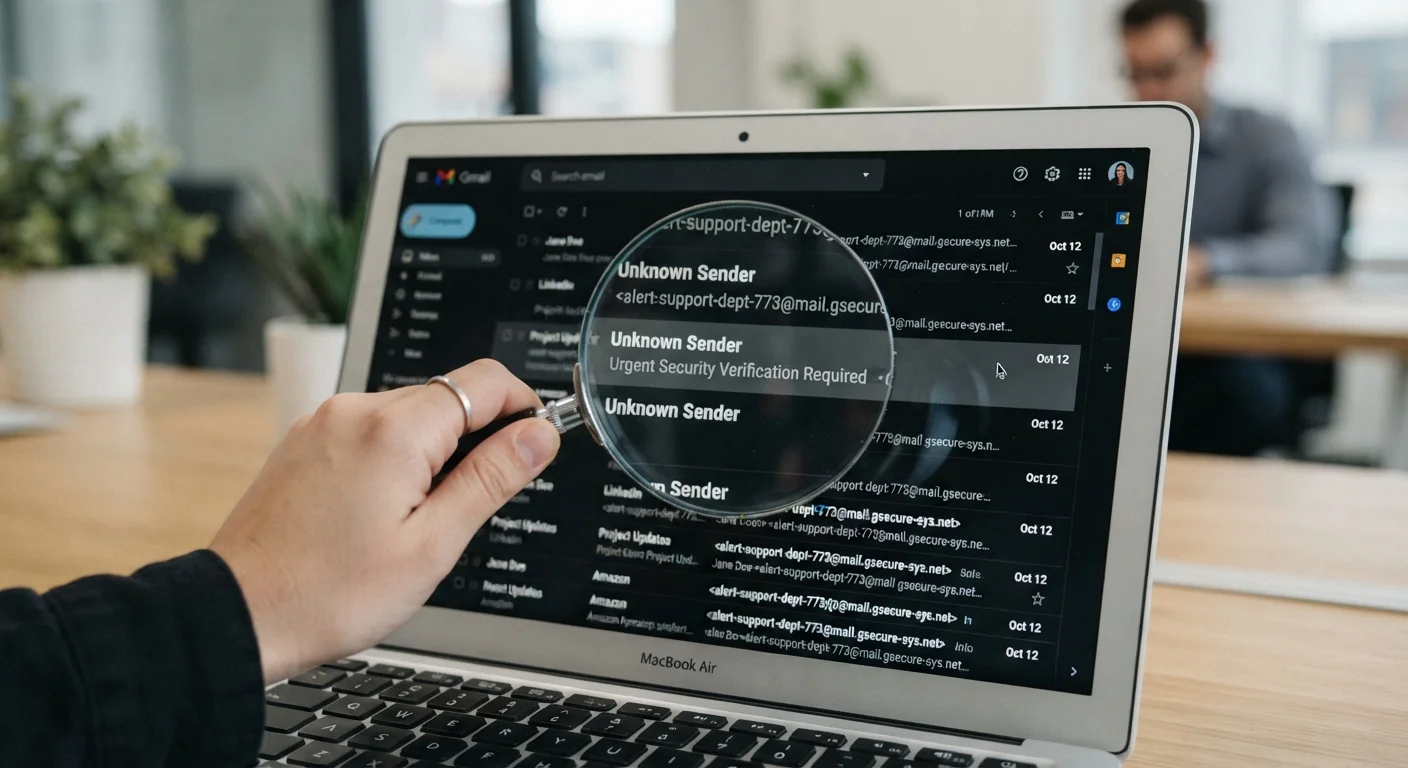
Photo: searchopenrecords editorial
—— In This Article
Key Takeaways
- Email addresses can be spoofed or fabricated; surface-level inspection alone is insufficient.
- Email headers reveal routing data that may expose mismatches between claimed and actual senders.
- Domain registration records can indicate whether a sending domain is legitimate or newly registered.
- Public record tools may help connect an address to a verifiable identity when used with appropriate caution.
- Cross-referencing multiple signals — not relying on any single check — produces the most reliable assessment.
Why Email Address Verification Matters
Receiving an email from an unfamiliar address puts you in an immediate credibility gap: the sender claims an identity, but you have no inherent reason to trust it. Email protocols were not designed with strong sender authentication in mind, which means anyone can construct a message that appears to come from a convincing address. Scammers, phishing actors, and simple cases of mistaken identity all land in the same inbox.
Understanding what public records can reveal about an email address is a useful starting point, but verification requires active steps beyond a single database query. The process below is structured to move from low-effort checks to progressively deeper investigation, so you can stop as soon as you have enough confidence — or continue if red flags accumulate.
What you will need
Step-by-Step: Assessing an Unknown Email Address
Follow these steps in order. Each builds on the last, and earlier checks will often surface enough information to reach a conclusion without completing every stage.
Inspect the sender address carefully
Look at the full email address — not just the display name. Display names are trivially set to anything; the actual address in angle brackets ([email protected]) is what matters. Watch for subtle substitutions: the numeral 1 for lowercase l, hyphens inserted into familiar brand names, or domains that mimic legitimate organizations with slight misspellings (e.g., paypa1.com instead of paypal.com).
Check the sending domain's registration history
Take the domain portion of the address (everything after the @) and query a WHOIS lookup service. A domain registered within the past few weeks or months, with privacy-masked registrant details and no associated web presence, is a meaningful warning sign. Established organizations typically operate on domains with multi-year histories. For a fuller explanation of how this data fits into email research, see domain registration data in email address research.
Examine the full email headers
Every email carries headers that log its routing path. Open the raw headers in your email client and look for the Received: chain, which lists each mail server the message passed through. Compare the originating server's domain against the claimed sender domain. A mismatch — for instance, a message claiming to be from a US bank but routed through an unrelated foreign server — is a strong indicator of spoofing or forwarding abuse.
Also check the Authentication-Results header for SPF, DKIM, and DMARC outcomes. A fail or none result on SPF means the sending server was not authorized by the domain's own records.
Search for the address in public records and aggregator tools
Run the email address through a reverse email lookup tool or people-search aggregator. These services compile data from publicly available sources — data breach disclosures, forum registrations, business filings, and similar records — to surface names, locations, or other identifiers historically associated with that address. A result that matches the sender's claimed identity adds credibility; no result is neutral; a result that contradicts the claimed identity warrants serious caution.
For a structured approach to this stage, the email lookup checklist for verifying unknown senders walks through each check in a repeatable format.
Corroborate through an independent channel
If the sender claims to represent a company, government agency, or organization, find contact information for that entity independently — through its official website or a directory, not through any link or number provided in the email itself. Reach out through that verified channel to confirm whether the message is legitimate. This step bypasses any infrastructure the sender controls and is the most reliable final check available.
When Verification Still Leaves Uncertainty
Even after completing every step, you may not arrive at certainty — and that is a realistic outcome worth accepting. Email addresses are easy to create and discard, legitimate senders sometimes use third-party platforms that produce unusual headers, and public record coverage of email-linked identity data is uneven.
If verification is inconclusive and the stakes are meaningful — financial, legal, or personal — treat the message with caution regardless. Responding with a request to verify identity through a separate channel (a phone number you independently look up, for example) is a reasonable next move. For a deeper look at connecting an address to a real person, see tracing an email address back to a person.
It is also worth noting that the same lookup infrastructure works in reverse: your own email address may be searchable. Protecting your own email address from reverse lookup covers the privacy practices that reduce your exposure.
Combine Email and Address Verification
If the suspicious sender includes a physical address, treat that as an additional data point to cross-reference. Our address verification checklist provides a parallel process for evaluating address claims against public records. Running both checks together significantly narrows the space of plausible sender identities.
People Search Editorial Team
People Search Editorial Team is the collective byline for our editorial team and contributor network. Articles published under this byline or an editorial pen name are researched, written, and reviewed according to our editorial standards for clarity, consistency, and independence before publication.
View author profile